Best Payment Processing for Contractors (2026 Guide)
Whether you’re an electrician, plumber, HVAC company, roofer, landscaper, painter, home renovator, or general contractor, getting paid quickly matters. Contractors often pay for labour,…
The Payment Card Industry Data Security Standard (PCI DSS) has always been the backbone of protecting cardholder data. With the release of PCI DSS v4.0 in March 2022, the standard underwent its most significant update in over a decade. While version 3.2.1 was officially retired in 2024, the real shift comes in March 2025, when all future-dated requirements move from “best practice” to mandatory compliance.
This transition is not just about ticking boxes, it introduces stronger authentication, better vulnerability management, and a move toward continuous security. For businesses that process payments, understanding what’s changing in 2025 is essential to avoid penalties and maintain customer trust.
The PCI Security Standards Council (PCI SSC) designed a multi-year transition plan so organizations could adapt gradually. This means businesses had time to test, refine, and implement new security measures before they became mandatory.
One of the most notable aspects of PCI DSS 4.0 is its sheer size. Compared with earlier versions, v4.0 expands the scope dramatically with new requirements designed to address today’s cyber threats.
The 2025 enforcement brings several high-impact changes that every organization handling cardholder data needs to prepare for. These updates touch everything from authentication to script monitoring, making the compliance bar much higher than before.
The scale of PCI DSS 4.0 is best understood through hard numbers. These figures highlight just how broad the changes are and why preparation is critical.
| Metric | 2022-2025 |
|---|---|
| New Requirements Introduced | 64 |
| Future-Dated (“Best Practice”) | 51 |
| Mandatory Enforcement Begins | March 31, 2025 |
| Password Length Requirement | 12 characters |
| Vulnerability Fix Scope | All severities |
| MFA Coverage | All CDE access |
The 2025 deadline isn’t just a regulatory milestone—it’s a turning point for payment security. With new rules around authentication, vulnerabilities, and payment scripts, businesses must be proactive to maintain trust and compliance.
If you process payments with Clearly Payments, PCI DSS compliance is part of keeping your business safe, trusted, and able to accept credit cards. With the March 31, 2025 deadline, merchants should be prepared:
At Clearly Payments, we work with merchants to simplify compliance:
Whether you’re an electrician, plumber, HVAC company, roofer, landscaper, painter, home renovator, or general contractor, getting paid quickly matters. Contractors often pay for labour,…
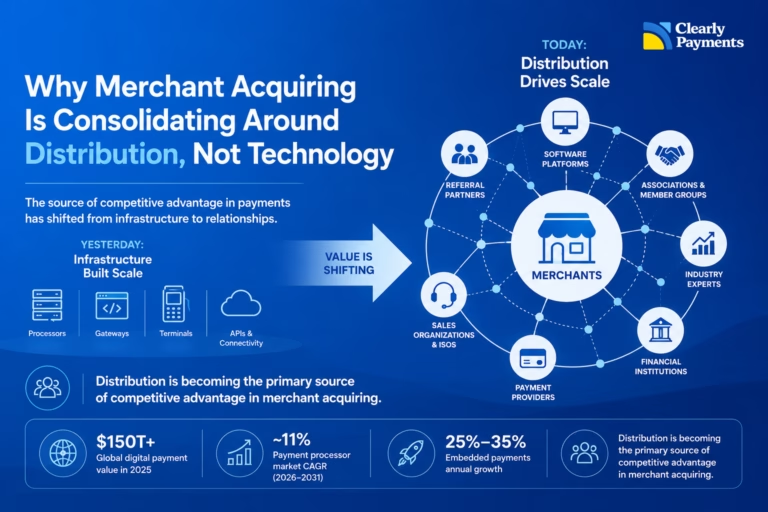
The payments industry has spent decades investing in technology. Processors built massive infrastructure platforms. Acquirers invested billions in connectivity, security, compliance, hardware certifications, and…
Accepting credit cards is essential for most businesses today, but the fees can quietly add up. Many merchants assume payment processing rates are fixed,…